What is SOC 2?
A SOC 2 report helps customers understand the controls behind your service. Start by agreeing on the system in scope, the report type, and the Trust Services categories that matter to the engagement.
Find what you need
- Scope: define the system boundary
- Preparation: work through the SOC checklist
- Evidence: understand what makes a useful record
- Report choices: compare SOC 1, SOC 2 and report types
On this page: How reporting works · Trust Services Criteria · Changes and timeline · FAQs · Ask for assistance
How SOC 2 reporting works
A CPA firm examines your system description and controls against the criteria agreed for the report. There are two report types:
- Type 1: Addresses the system description and whether controls are suitably designed at a specified date. It does not provide an opinion on operating effectiveness.
- Type 2: Also addresses whether controls operated effectively over the stated period. The report includes the auditor’s tests and results.
Customers use this information to assess the services they outsource. SOC 2 covers the Trust Services categories included in the examination. SOC 1 instead addresses controls relevant to customers’ financial reporting.
See the AICPA SOC 2 guide, section 1.05 for the report-type distinction.
What are the Trust Services Criteria?
The Trust Services Criteria are the benchmarks used to evaluate controls in a SOC 2 examination. They cover five categories: Security, Availability, Processing Integrity, Confidentiality, and Privacy. Your controls are the policies and activities you put in place to meet the applicable criteria. Points of focus help explain the criteria; they are not a separate checklist every organization must satisfy item by item.
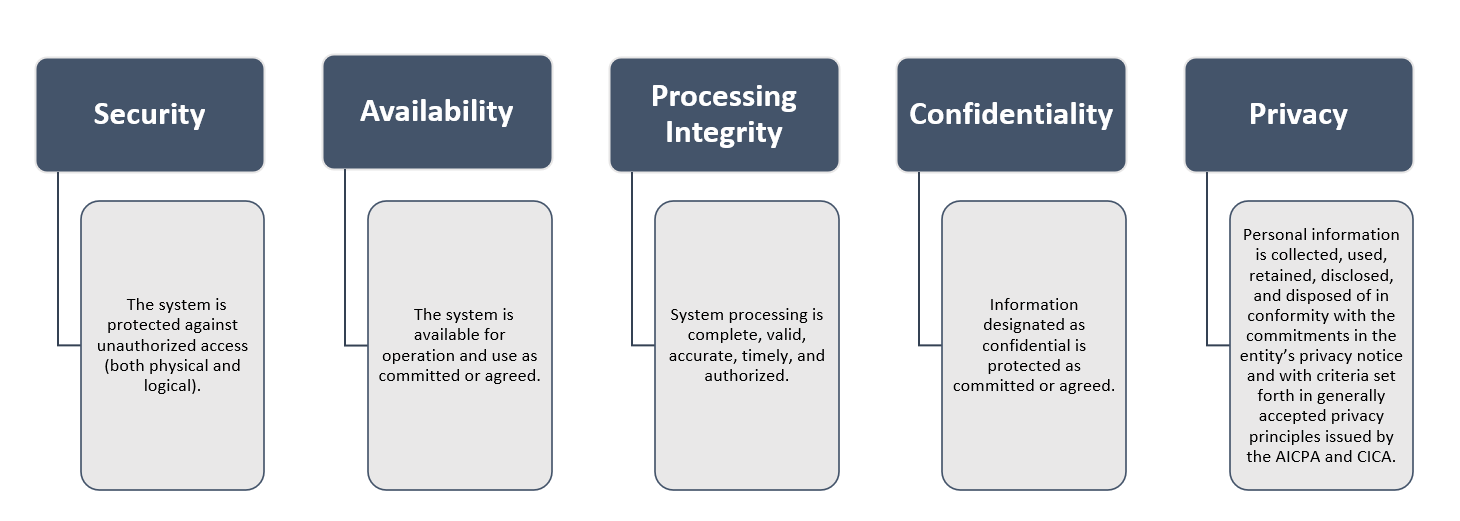
The five categories, in plain language
The diagram above uses older terminology. This readable summary follows the AICPA’s 2017 Trust Services Criteria with revised points of focus (2022).
- Security: Protect systems and data from unauthorized access, disclosure, and damage.
- Availability: Keep systems and information usable as needed to meet the organization’s objectives.
- Processing integrity: Check that processing is complete and accurate, valid and authorized, and finished on time.
- Confidentiality: Protect information the organization has designated as confidential.
- Privacy: Manage how personal information is collected, used, kept, shared, and disposed of in line with the organization’s privacy objectives.
A SOC 2 report does not necessarily cover all five categories. Check the categories and system boundaries in the report; agree the intended scope with your auditor.
Further reading: AICPA: 2017 Trust Services Criteria with revised points of focus (2022).
Changes to SOC 2
The 2022 revision updated the points of focus, not the 2017 criteria themselves. It adds guidance on changing technology risks and privacy expectations. It also explains data management and the different responsibilities of organizations that control or process personal information.
Agree the applicable criteria and system scope with your auditor. The timeline below separates past changes from proposals that are not yet final.
SOC 2 Change Timeline

Read the SOC 2 timeline and sources
- 2011 — SOC reporting suite: SOC 1, SOC 2 and SOC 3 reporting were introduced. AICPA history.
- 2017–2018 — Updated criteria: The Trust Services Criteria aligned with COSO’s 2013 framework. The transition ended in December 2018. AICPA criteria; AICPA SOC 2 guide, footnote 15.
- 2022 — Revised points of focus: Supporting guidance changed; the 2017 criteria remained unchanged. AICPA criteria and revision notice.
- October 2026 — Proposed 2027 update: AICPA released draft revisions for comment. These are proposals, not final requirements. AICPA proposal announcement.
Proposal status checked November 2, 2026.
Need to address another framework alongside SOC 2? Read about SOC 2 with additional subject matter. Discuss the proposed scope and suitable criteria with your auditor. A framework mapping alone does not establish compliance.
The report covers the categories and system agreed for the examination, not necessarily all five categories. SaaS providers, data centers and other service organizations should choose scope based on their services and customer needs.

